Pinned
English
Weaponizing Google Chrome Update Service for Execution & Persistence
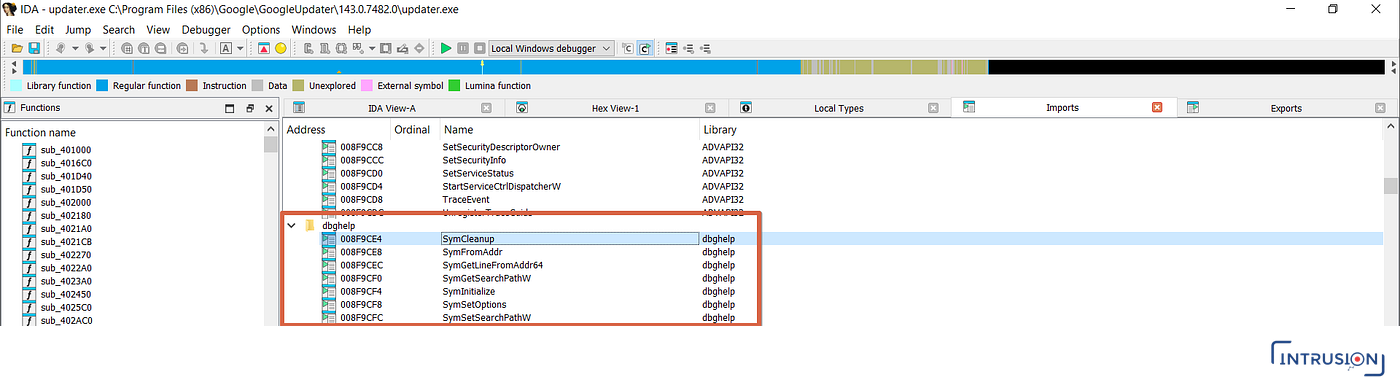
A weekend Process Monitor boot log turned into a full DLL side-loading study: finding a hijackable load in Google's updater service, building and stabilizing a PoC with a DLL proxy, turning it into SYSTEM persistence, and the detection and forensic opportunities it leaves behind.
Read Post