
Designed here, from the ground up.
Every curriculum is designed here, over months, from years of casework and from watching where analysts get stuck.

Tools change every year. How an intrusion works, and how it is analysed, does not. The book says one thing, the SOC/DFIR floor says another. We teach both.
Ten standards behind every course we teach. We hold to them on every lesson, for every batch.
Every curriculum is designed here, over months, from years of casework and from watching where analysts get stuck.

Networking, operating systems and Windows internals are the core of every course, not the warm-up. You learn where a tool's data is born, the process, the registry, the log, before you touch the tool. Then the dashboard stops being magic.


DNS exists because one text file stopped scaling. Firewalls exist because perimeters failed. Learn what broke, and you understand the fix down to its design.


Every attack you study happened: in incidents we worked ourselves, or in investigations published by trusted sources. Current, cited, and real.


Before you learn to defend, you plan the attack. You can't detect, or investigate, what you can't imagine.


The book says one thing, real SOCs say another. Every lesson is written by someone who does the job, and shows you both.


Reading before every session, homework after, and parts you study alone before you ask. The field needs analysts who can carry the weight.


Each course names what it does not cover and exactly where to learn it next. An analyst who knows their gaps is safer than one who thinks they are complete.


AI will always know more facts than you. We train what it can't: reading context, forming a hypothesis, doubting the obvious answer. And we show where AI helps, and where it misleads.


Every course also teaches the market: the skills teams hire for, the gaps they cannot fill, and what the job really asks of you. Then we help you get there, with CV reviews, interview practice and introductions. A stronger analyst, a better-staffed SOC, a healthier market: everyone has to win.

I hold every course we teach to these standards. If you find one we broke, tell me directly.
Each course has a code, like IR-200. Courses in a track build on each other, but you do not have to take them all in order: start where you need to, as long as you already know what the earlier ones teach.
Live sessions with the person who wrote the course. Reading before each one, homework after.
Systems Internals, Enterprise Infrastructure, Adversary Tradecrafts, Analysis Process & Much More
To be announced soon.
The same curriculum at your own pace: lessons, labs and quizzes. Buy once, or start free, and keep it.
Standalone sessions on how analysts think: storytelling, context, the Pyramid of Pain and pivoting
A series of standalone sessions on how analysts really think: reading an intrusion as a story, building context, going after the indicators that hurt the attacker, and pivoting without getting lost.
A practical incident response series: one intrusion, followed from the first alert to the domain controller
Follow Rider.exe through a real intrusion, from Tier 1 triage in Elastic to PsExec, identity, file and network telemetry, and the incident response decisions along the way. New episodes are added as the series continues.
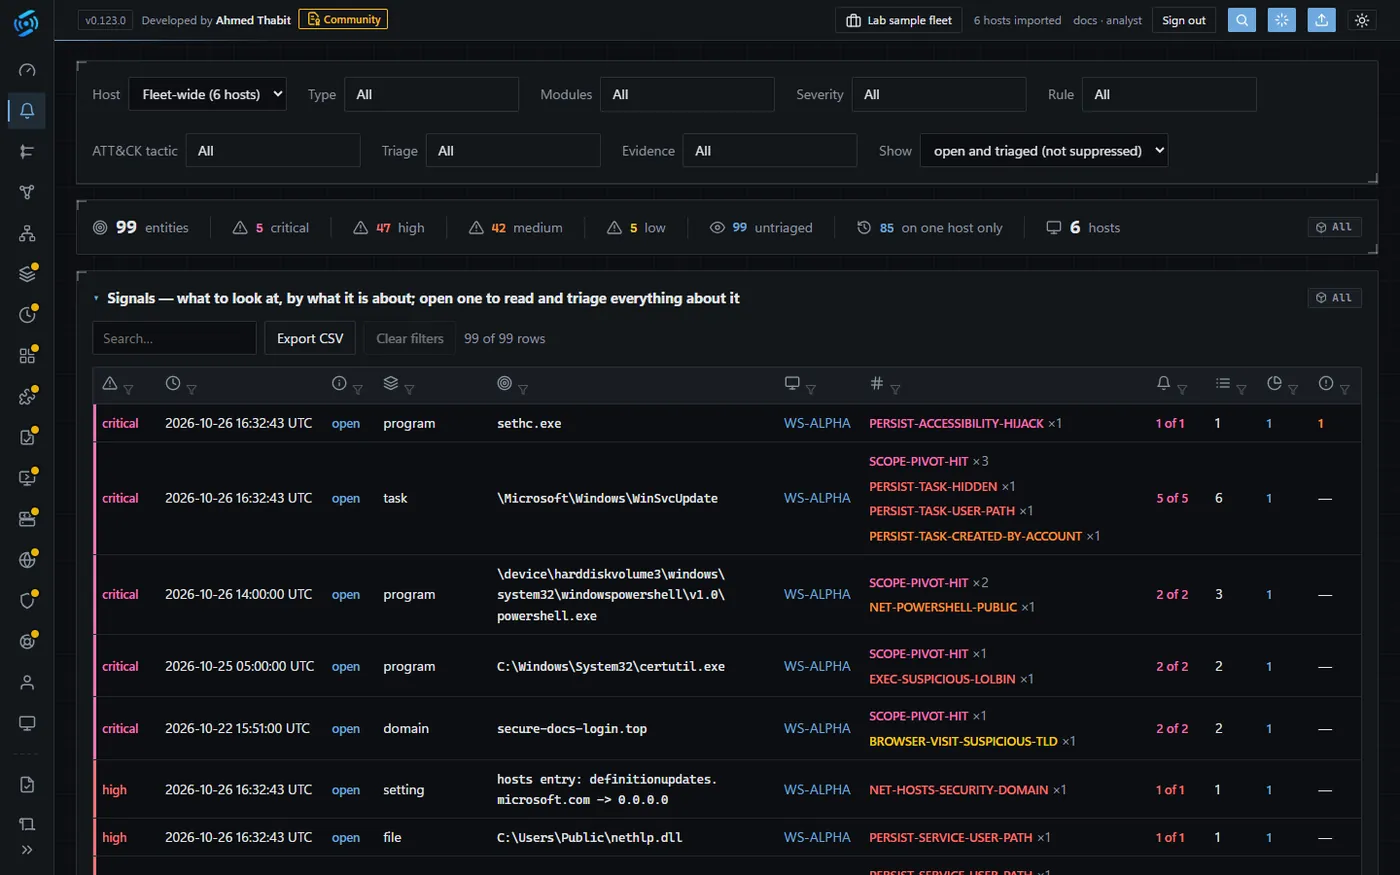
Signal came out of the same casework as the courses. It is the first minute of an investigation, done for you.
 DFIR survey tool
Hours of triage, distilled into one: where to look, and what you can't see. Read-only, about a minute on Windows 10, 11 and Server.
Write-ups from cases and labs, and answers to the questions students asked that we couldn't answer on the spot.
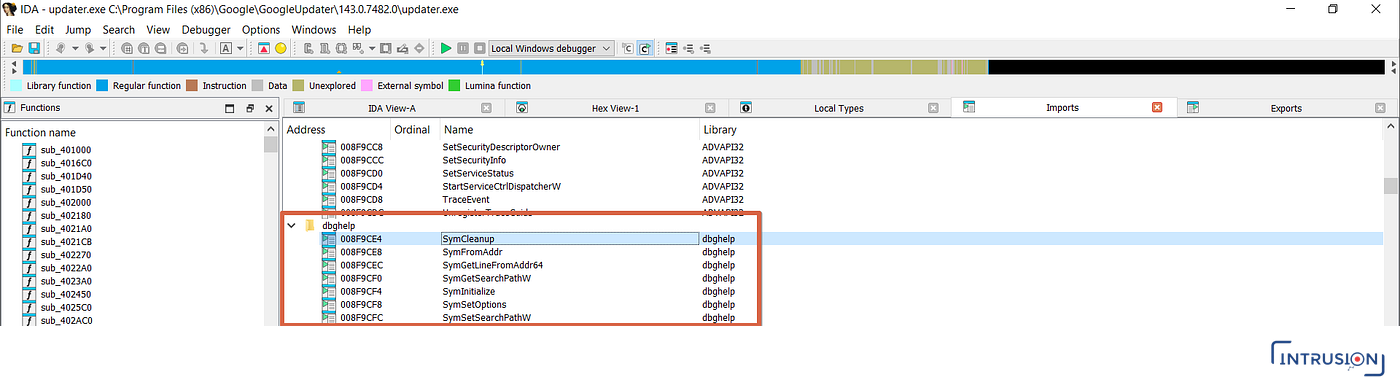
A weekend Process Monitor boot log turned into a full DLL side-loading study: finding a hijackable load in Google's updater service, building and stabilizing a PoC with a DLL proxy, turning it into SYSTEM persistence, and the detection and forensic opportunities it leaves behind.
Read Post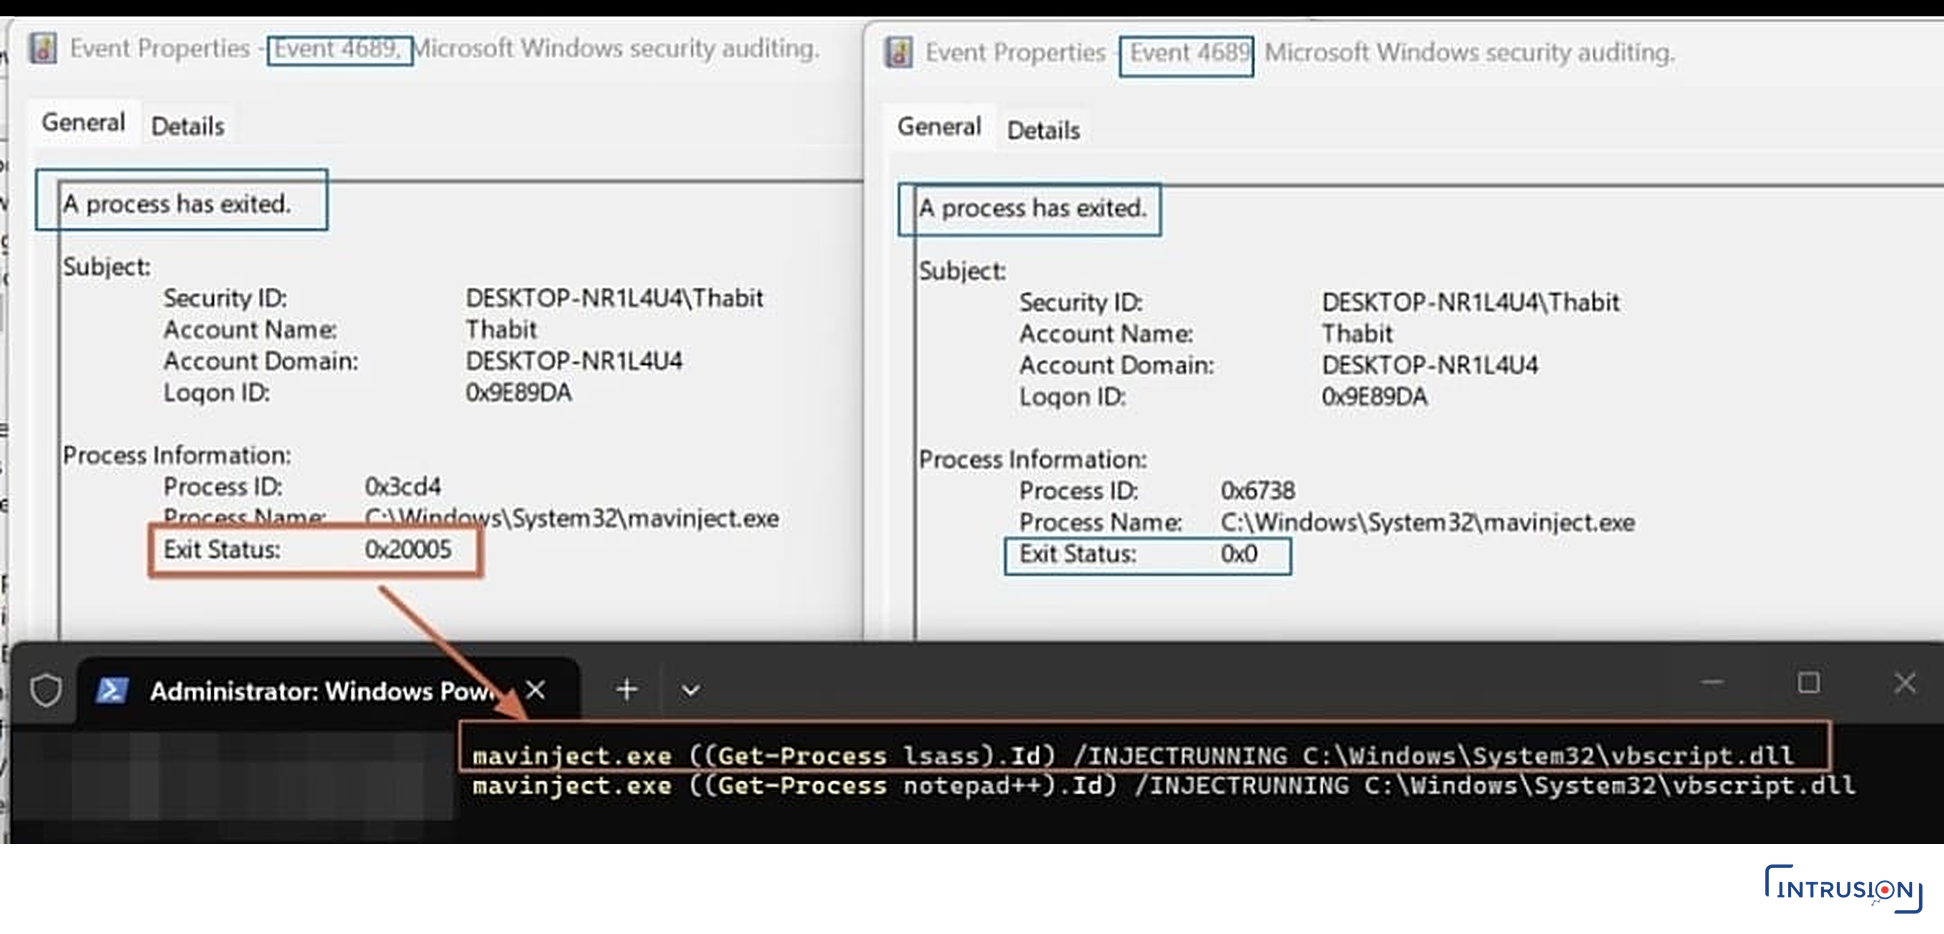
Reproducing Red Canary's mavinject.exe injection into LSASS on Windows 11: why PPL makes it fail, why Sysmon Event ID 7 only shows the successful injection, and how Event 4689 exit codes tell success from failure when the tool stays silent.
Read Post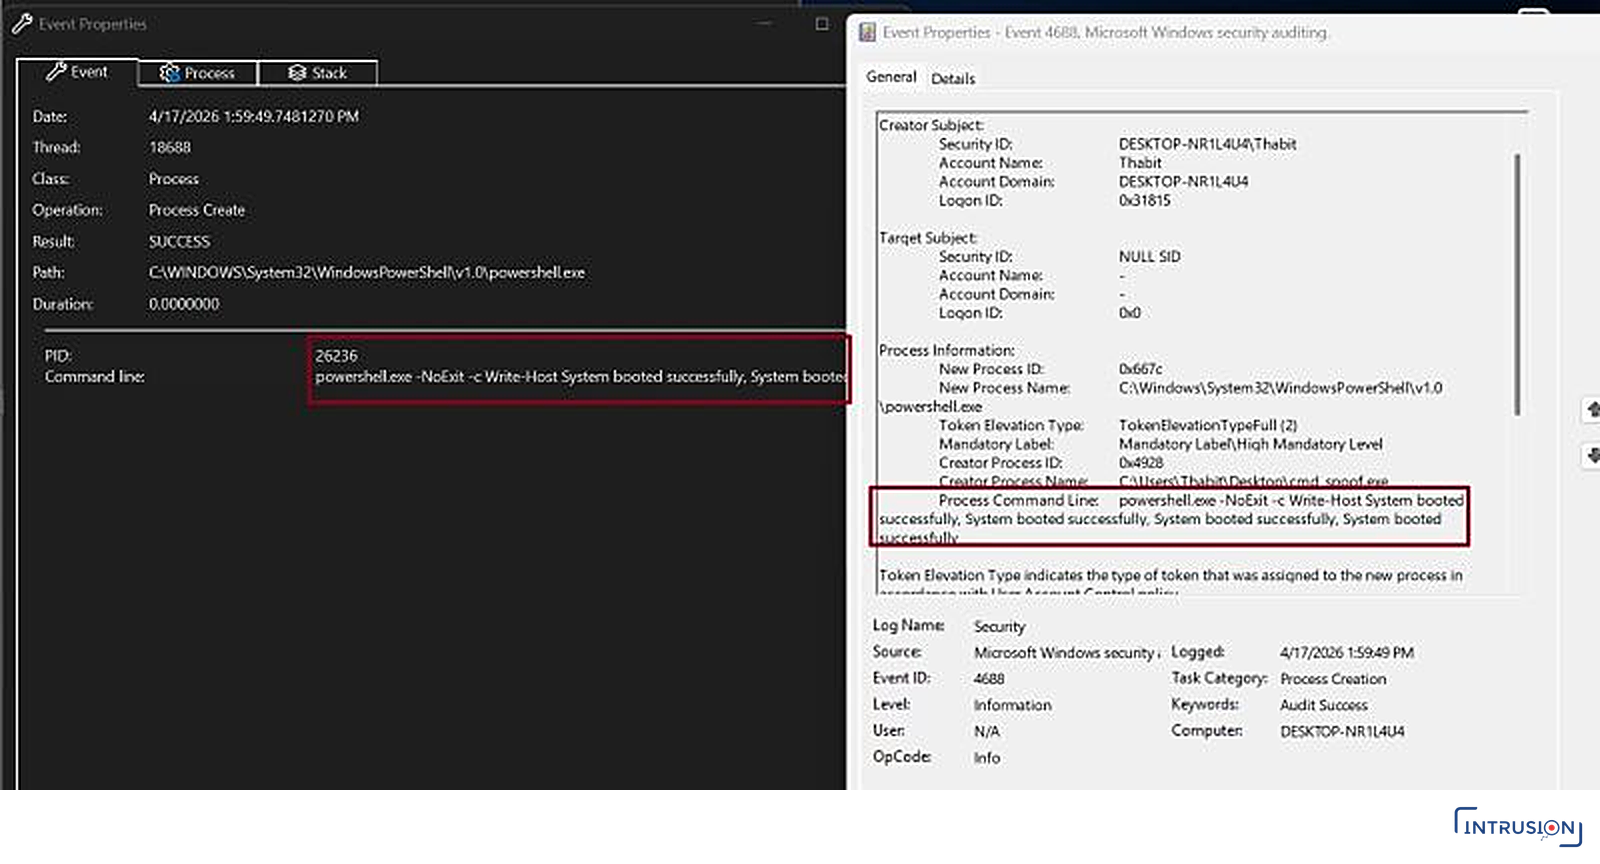
A weekend PoC that starts PowerShell suspended with a harmless command line, rewrites the command line in its PEB and resumes it: Security 4688 and Procmon log Write-Host while PowerShell downloads an executable. How it works, the length-field trick, and how to catch it with context.
Read Post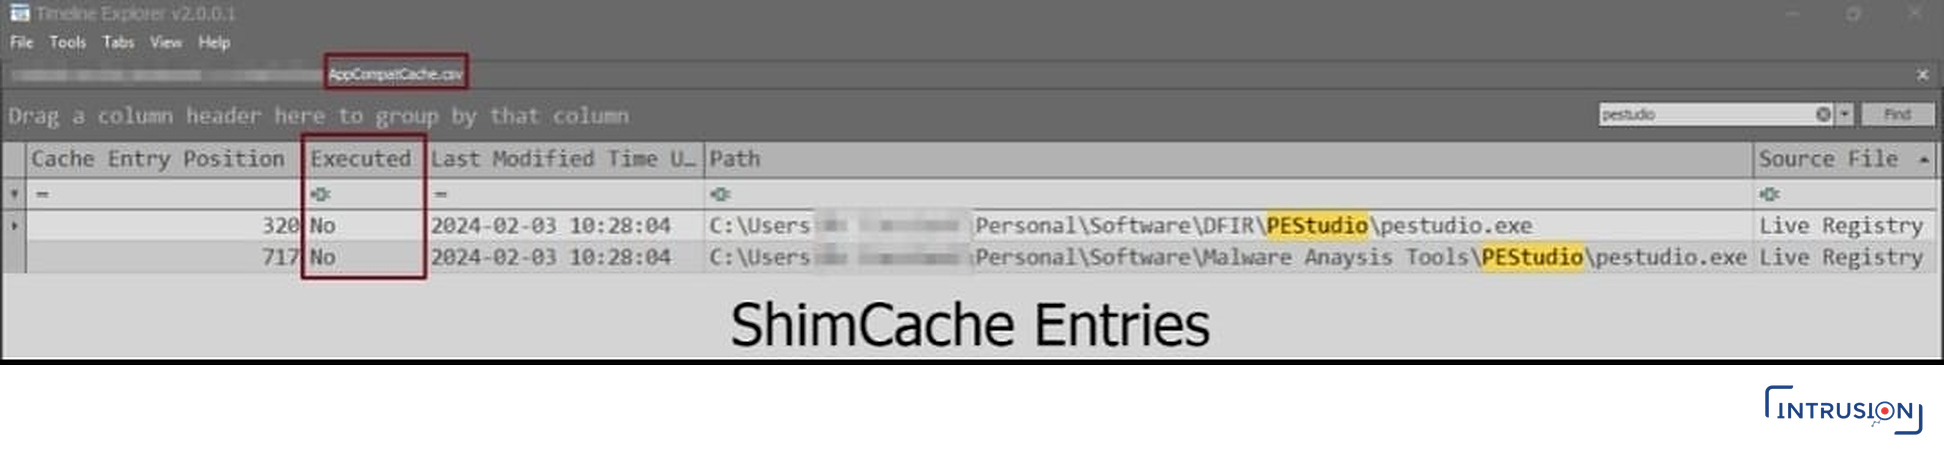
A ShimCache entry does not mean the program ran. Walking through AppCompatCacheParser's "Executed" column, a Prefetch cross-check, the last-four-bytes assumption and where it breaks down — and why you must understand how an artifact and its tools really work before you conclude.
Read PostFor SOC, DFIR and security teams. The same standards, built around your environment.
Tell us where your analysts are and where they need to be. We design the path from your stack and your incidents, teach it with the people who wrote it, and show you what each analyst can now do.
We map the courses to your tools, your log sources and each analyst's level, and cut what your team won't use.
Your team only, on the days and hours your rota allows. Reading before, homework after, like every batch.
We rebuild the attacks your team has seen, or should expect, so they practise on what will actually reach them.
Quiz and lab results for every analyst: what they can investigate now, not how many hours they sat.